NimblePlugins WordPress tool
Security — Free
Complete WordPress security you host yourself: two-factor authentication, integrity monitoring, a web application firewall, local malware scanning, quarantine and incident response — free, forever, with no telemetry.
Self-hosted · No telemetry · GPL licensed
Nimble Security is the protection layer in the NimblePlugins suite, and it is complete on its own. It owns every enforcement engine on your site: identity, file integrity, firewall, malware detection, incident response and recovery. There is no licence to enter and no account to create — if you never buy Pro, nothing here is withheld from you.
Identity
- Brute-force protection — per-IP and per-account lockouts with configurable thresholds and windows, plus generic login errors so an attacker cannot tell a wrong username from a wrong password.
- Two-factor authentication — encrypted TOTP secrets, enrolment by QR code generated locally or by manual entry, ten single-use recovery codes, and replay protection that refuses a code already spent.
- Session and credential control — see and revoke WordPress sessions, audit and revoke application passwords, and optionally shut off authenticated XML-RPC.
- Author enumeration protection — anonymous
?author=probes return a 404 instead of revealing usernames.
Integrity
- WordPress core verification against the official checksum service.
- SHA-256 baselines for plugins, themes, must-use plugins, drop-ins and selected configuration files, scanned in resumable background passes that survive timeouts.
- Update Intelligence — when WordPress confirms a plugin or theme was installed, updated, activated or deleted, the resulting file changes are correlated with that maintenance instead of being reported as a compromise.
- Honest severity — a changed
.htaccessor cache drop-in is presented for review, not labelled malware. You can mark recognised changes intentional. Core checksum failures and strong evidence can never be dismissed that way.
Firewall
- Protect, Learning or Off — twelve high-confidence rules covering traversal, local file inclusion, SQL injection, cross-site scripting, dangerous stream wrappers, executable upload probes and sensitive file access.
- Enforced through WordPress — every rule above is applied by the plugin itself. It generates no PHP file and never touches your server configuration. The optional pre-WordPress layer via PHP
auto_prepend_file, Extended Protection, ships with Nimble Security Pro. - Correct client IP handling — forwarded headers are honoured only when you have declared trusted proxies, so a spoofed header cannot frame an innocent visitor.
- Optional rate limiting with a configurable per-minute budget.
Malware and vulnerabilities
- Local malware scanning — resumable background workers with a WP-Cron fallback and a watchdog that restarts a stalled scan. Your files are read on your server and never uploaded anywhere.
- Software inventory for core, plugins and themes, with a strict provider contract for authoritative advisories. Free does not pretend to ship a real-time vulnerability feed — it tells you what you have installed and what it can actually verify.
Response and recovery
- Encrypted quarantine — AES-256-GCM, stored locally. The file is re-hashed immediately before it is moved and the written vault copy is verified before the original is removed, so a file that changed after detection is never quarantined from stale evidence.
- Component containment — deactivate a whole affected plugin rather than surgically deleting a file out from under running code.
- Emergency Lockdown — freeze plugin installs, theme edits, file modification, application passwords and user creation, while preserving exactly one rescue administrator session so you cannot lock yourself out.
- Recovery Readiness — a 10-point score built from your backup provider's aggregate health. Destructive response asks for a recovery point first, and every action is followed by a fresh verification scan.
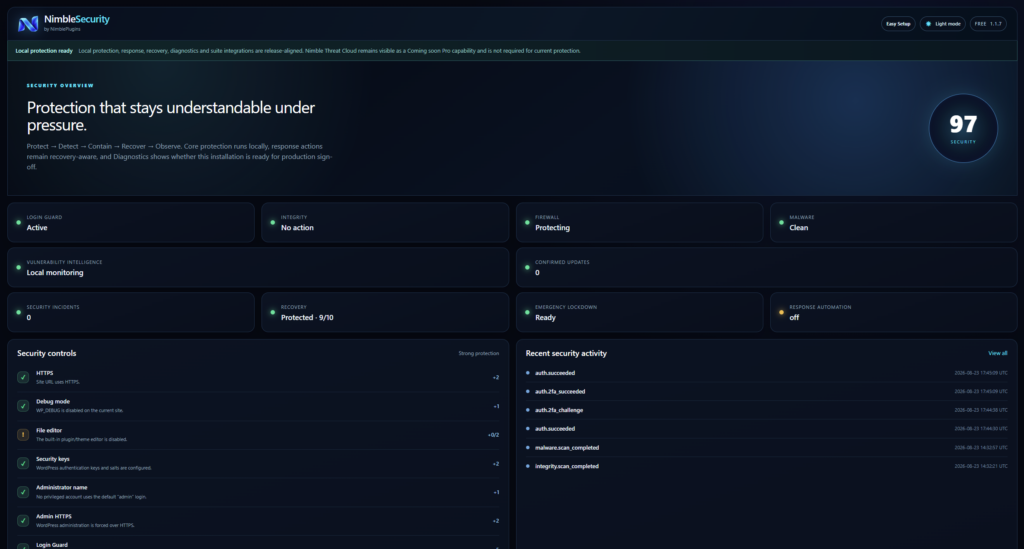
Security Score
A 100-point posture score across hardening, identity, integrity, firewall, malware detection, software updates and recovery readiness. An open high or critical incident caps the score, so a site actively under attack can never display a comfortable number.
Privacy
Scanning runs locally and file contents are never uploaded. Security events store no request bodies, cookies or credentials, and network actors are recorded as keyed hashes rather than raw IP addresses. Two-factor secrets are encrypted at rest and are excluded from WordPress personal-data exports. The only outbound request Free makes is to the official WordPress.org checksum service, and it sends nothing but your core version and locale.
Self-hosted. No telemetry. GPL licensed. WordPress 6.6+, PHP 8.1+.